


[Oct-2021] Microsoft AZ-400 Exam: Basic Questions With Answers
New 2021 Realistic Free Microsoft AZ-400 Exam Dump Questions & Answer
What Is AZ-400 Exam?
Passing AZ-400 test will get you the Microsoft Certified: DevOps Engineer Expert certification, which is one of the latest role-based Azure certificates that will verify the knowledge and skills of the candidates seeking Azure DevOps expertise. It is designed to equip the specialists with the needed skills to function as DevOps engineers who provide an organization with the best solutions. Those students who pass such an exam will be able to prove their skills and knowledge and officially verify them. You should be aware that there will be 40-60 questions in the Microsoft AZ-400 that you will have to attempt within 180 minutes. The type of questions that will come in such an exam may include multiple-choice, case studies, review screen, hot area, fill-in-the-blank, drag and drop, active screen, and other types of questions. This test can be taken in different languages, including English, Korean, Japanese, and Simplified Chinese. To clear it, you will have to get the passing score of 700 marks. Sitting for the certification test costs $165. To register for it, visit the official site and follow the instructions indicated there.
Benefits of having MICROSOFT AZ-400 Certifications
Getting a certification like AZ-400 can enhance the value of a job aspirant as a qualified Azure DevOps Engineer It’d really attract HR to have a look to your CV and definitely it will help you out to have good salaried job in your hand by the end of the day. In such a situation, the relevance of a quality AZ-400 Microsoft Azure DevOps Solutions Exam study material is extremely important. The relevance of a quality MICROSOFT AZ-400 Exam study material is extremely important. And so we bring best-in-industry MICROSOFT AZ-400 Exam online course and practice tests for you to help in your exam preparation.
Microsoft Azure DevOps Solutions AZ-400 Dumps Provided Study Notes
Pass4guide expert team recommend you to prepare some notes on these topics along with it don’t forget to practice Microsoft Azure DevOps Solutions AZ-400 Dumps which been written by our expert team Both these will help you a lot to clear this exam with good marks.
- Multi-agent builds
- Azure DevOps
- Azure Kubernetes Service
- Integrate secrets
- Ansible
- Code (IaC) strategy
- Puppet
- Code technologies
- HockeyApp
- Terraform
- Analyze telemetry
NEW QUESTION 66
You have an Azure DevOps organization that contains a project named Project1.
You need to create a published wiki in Project1.
What should you do first?
- A. Modify the Storage settings of Project1.
- B. Modify the Team configuration settings of Project1.
- C. In Project1, create an Azure DevOps pipeline.
- D. In Project1, create an Azure DevOps repository.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/devops/project/wiki/publish-repo-to-wiki?view=azure-devops&tabs=brow
NEW QUESTION 67
You are developing an open source solution that uses a GitHub repository.
You create a new public project in Azure DevOps.
You plan to use Azure Pipelines for continuous build. The solution will use the GitHub Checks API.
Which authentication type should you use?
- A. a personal access token
- B. GitHub App
- C. OAuth
- D. SAML
Answer: C
Explanation:
You can authenticate as a GitHub App.
References: https://developer.github.com/apps/building-github-apps/authenticating-with-github-apps/
NEW QUESTION 68
You company uses Azure DevOps to deploy infrastructures to Azure.
Pipelines are developed by using YAML.
You execute a pipeline and receive the results in the web portal for Azure Pipelines as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Reference:
https://dev.to/rajikaimal/azure-devops-ci-cd-yaml-pipeline-4glj
NEW QUESTION 69
Your team uses an agile development approach.
You need to recommend a branching strategy for the team's Git repository. The strategy must meet the following requirements.
* Provide the ability to work on multiple independent tasks in parallel.
* Ensure that checked-in code remains in a releasable state always.
* Ensure that new features can be abandoned at any time.
* Encourage experimentation.
What should you recommend?
- A. multiple long-running branches
- B. a single long-running branch without forking
- C. a single fork per team member
- D. a single long-running branch with multiple short-lived topic branches
Answer: D
Explanation:
Topic branches, however, are useful in projects of any size. A topic branch is a short-lived branch that you create and use for a single particular feature or related work. This is something you've likely never done with a VCS before because it's generally too expensive to create and merge branches. But in Git it's common to create, work on, merge, and delete branches several times a day.
Reference:
https://git-scm.com/book/en/v2/Git-Branching-Branching-Workflows
NEW QUESTION 70
You have an Azure Kubermets Service (AKS) implementation that is RBAC-enabled
You plan to use Azure Container Instances as a hosted development environment to run containers in the AKS implementation.
You need to conjure Azure Container Instances as a hosted environment for running me containers in AKS. Which three actions should you perform m sequence?
To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation:
Step 1: Create a YAML file.
If your AKS cluster is RBAC-enabled, you must create a service account and role binding for use with Tiller. To create a service account and role binding, create a file named rbac-virtual-kubelet.yaml
Step 2: Run kubectl apply.
Apply the service account and binding with kubectl apply and specify your rbac-virtual-kubelet.yaml file.
Step 3: Run helm init.
Configure Helm to use the tiller service account:
helm init --service-account tiller
You can now continue to installing the Virtual Kubelet into your AKS cluster.
References:
https://docs.microsoft.com/en-us/azure/aks/virtual-kubelet
NEW QUESTION 71
Your company uses cloud-hosted Jenkins for builds.
You need to ensure that Jenkins can retrieve source code from Azure Repos.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create a service hook in Azure DevOps.
- B. Create a webhook in Jenkins.
- C. Create a personal access token in your Azure DevOps account.
- D. Add a domain to your Jenkins account.
- E. Add the Team Foundation Server (TFS) plug-in to Jenkins.
Answer: A,C,E
Explanation:
Explanation/Reference:
Explanation:
B: Jenkins’ built-in Git Plugin or Team Foundation Server Plugin can poll a Team Services repository every few minutes and queue a job when changes are detected.
D: Use Azure DevOps/ Visual Studio Team Services to create an access token, and use th E: For those who need tighter integration, Team Services provides two additional ways to achieve it: 1) the Jenkins Service Hook, and 2) Jenkins build and release tasks.) References:
https://blogs.msdn.microsoft.com/devops/2017/04/25/vsts-visual-studio-team-services-integration-with- jenkins/
http://www.aisoftwarellc.com/blog/post/how-to-setup-automated-builds-using-jenkins-and-visual-studio- team-foundation-server/2044
NEW QUESTION 72
How should you confrere the release retention policy for the investment planning depletions suite? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Every request made against a storage service must be authorized, unless the request is for a blob or container resource that has been made available for public or signed access. One option for authorizing a request is by using Shared Key.
Scenario: The mobile applications must be able to call the share pricing service of the existing retirement fund management system. Until the system is upgraded, the service will only support basic authentication over HTTPS.
The investment planning applications suite will include one multi-tier web application and two iOS mobile application. One mobile application will be used by employees; the other will be used by customers.
References: https://docs.microsoft.com/en-us/rest/api/storageservices/authorize-with-shared-key
Topic 2, Overview
Existing Environment
Contoso, Ltd. is a manufacturing company that has a main office in Chicago.
Requirements
Contoso plans to improve its IT development and operations processes implementing Azue DevOps principles. Contoso has an Azure subscription and creates an Azure DevOPs organization.
The Azure DevOps organization includes:
* The Docker extension
* A deployment pool named Pool7 that contains 10 Azure virtual machines that run Windows Server 2016.
The Azure subscription contains an Azure Automation account.
Planned Changes
Contoso plans to create projects in Azure DevOps as shown in the following table.
Technical Requirements
Contoso identities the following technical requirements:
* Implement build agents rot Project 1.
* Whenever possible, use Azure resources
* Avoid using deprecated technologies
* Implement a code flow strategy for Project2 that will:
* Enable Team 2 to submit pull requests for Project2.
* Enable Team 2 to work independently on changes to a copy of Project?
* Ensure that any intermediary changes performed by Tram2 on a copy of Project2 will be subject to the same restrictions as the ones defied in the build policy of Project2.
* Whenever possible. Implement automation and minimize administrative effort.
* Implement Protect3, Project5, Project6, and Project7 based on the planned changes.
* Implement Project4 and configure the project to push Docker images to Azure Container Reentry.
NEW QUESTION 73
You have a project in Azure DevOps.
You plan to deploy a self-hosted agent by using an unattended configuration script.
Which two values should you define in the configuration script? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. the organization URL
- B. the deployment group name
- C. the project name
- D. authorization credentials
- E. the agent pool name
Answer: A,D
Explanation:
Unattended config:
The agent can be set up from a script with no human intervention. You must pass --unattended and the answers to all questions.
To configure an agent, it must know the URL to your organization or collection and credentials of someone authorized to set up agents. All other responses are optional.
Reference:
https://docs.microsoft.com/en-us/azure/devops/pipelines/agents/v2-windows Overview
NEW QUESTION 74
You manage a website that uses an Azure SQL Database named db1 in a resource group named RG1lod11566895.
You need to modify the SQL database to protect against SQL injection.
To complete this task, sign in to the Microsoft Azure portal.
Answer:
Explanation:
See solution below.
Explanation
Set up Advanced Threat Protection in the Azure portal
1. Sign into the Azure portal.
2. Navigate to the configuration page of the server you want to protect. In the security settings, select Advanced Data Security.
3. On the Advanced Data Security configuration page:
4. Enable Advanced Data Security on the server.
Note: Advanced Threat Protection for Azure SQL Database detects anomalous activities indicating unusual and potentially harmful attempts to access or exploit databases. Advanced Threat Protection can identify Potential SQL injection, Access from unusual location or data center, Access from unfamiliar principal or potentially harmful application, and Brute force SQL credentials Reference:
https://docs.microsoft.com/en-us/azure/storage/common/storage-account-create
https://docs.microsoft.com/en-us/azure/azure-sql/database/threat-detection-configure
NEW QUESTION 75
You need to configure the alert for VM1. The solution must meet the technical requirements.
Which two settings should you configure? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION 76
You create a Microsoft ASP.NET Core application.
You plan to use Azure Key Vault to provide secrets to the application as configuration data.
You need to create a Key Vault access policy to assign secret permissions to the application. The solution must use the principle of least privilege.
Which secret permissions should you use?
- A. List only
- B. Get only
- C. Get and List
Answer: B
Explanation:
Application data plane permissions:
* Keys: sign
* Secrets: get
Reference:
https://docs.microsoft.com/en-us/azure/key-vault/key-vault-secure-your-key-vault Implement Continuous Integration Testlet 1 Case Study This is a case study. Case studies are not timed separately. You can use as much exam time as you would like to complete each case. However, there may be additional case studies and sections on this exam. You must manage your time to ensure that you are able to complete all questions included on this exam in the time provided.
To answer the questions included in a case study, you will need to reference information that is provided in the case study. Case studies might contain exhibits and other resources that provide more information about the scenario that is described in the case study. Each question is independent of the other question on this case study.
At the end of this case study, a review screen will appear. This screen allows you to review your answers and to make changes before you move to the next sections of the exam. After you begin a new section, you cannot return to this section.
To start the case study
To display the first question on this case study, click the Next button. Use the buttons in the left pane to explore the content of the case study before you answer the questions. Clicking these buttons displays information such as business requirements, existing environment, and problem statements. If the case study has an All Information tab, note that the information displayed is identical to the information displayed on the subsequent tabs. When you are ready to answer a question, click the Question button to return to the question.
Overview
Contoso, Ltd. is a manufacturing company that has a main office in Chicago.
Existing Environment
Contoso plans to improve its IT development and operations processes by implementing Azure DevOps principles. Contoso has an Azure subscription and creates an Azure DevOps organization.
The Azure DevOps organization includes:
* The Docker extension
* A deployment pool named Pool7 that contains 10 Azure virtual machines that run Windows Server 2016 The Azure subscription contains an Azure Automation account.
Requirements
Planned changes
Contoso plans to create projects in Azure DevOps as shown in the following table.
Technical requirements
Contoso identifies the following technical requirements:
* Implement build agents for Project1.
* Whenever possible, use Azure resources.
* Avoid using deprecated technologies.
* Implement a code flow strategy for Project2 that will:
-Enable Team2 to submit pull requests for Project2.
-Enable Team2 to work independently on changes to a copy of Project2.
-Ensure that any intermediary changes performed by Team2 on a copy of Project2 will be subject to the same restrictions as the ones defined in the build policy of Project2.
* Whenever possible, implement automation and minimize administrative effort.
* Implement Project3, Project5, Project6, and Project7 based on the planned changes.
* Implement Project4 and configure the project to push Docker images to Azure Container Registry.
NEW QUESTION 77
You are implementing an Azure DevOps strategy for mobile devices using App Center.
You plan to use distribution groups to control access to releases.
You need to create the distribution groups shown in the following table.
Which type of distribution group should you use for each group? To answer, drag the appropriate group types to the correct locations. Each group type may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Box1: Private
In App Center, distribution groups are private by default. Only testers invited via email can access the releases available to this group.
Box 2: Public
Distribution groups must be public to enable unauthenticated installs from public links.
Box 3: Shared
Shared distribution groups are private or public distribution groups that are shared across multiple apps in a single organization.
Reference:
https://docs.microsoft.com/en-us/appcenter/distribution/groups
NEW QUESTION 78
Your company plans to deploy an application to the following endpoints:
* Ten virtual machines hosted in Azure.
* Ten virtual machines hosted in an on-premises data center environment All the virtual machines have the- Azure Pipelines agent.
You need to implement a release strategy for deploying the application to the endpoints.
What should you recommend using to deploy the application to the endpoints? To answer, drag the appropriate components to the correct endpoint.
Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or soon to view content NOTE: Each correct selection n worth one point.
Answer:
Explanation:
Explanation
Box 1: A deployment group
When authoring an Azure Pipelines or TFS Release pipeline, you can specify the deployment targets for a job using a deployment group.
If the target machines are Azure VMs, you can quickly and easily prepare them by installing the Azure Pipelines Agent Azure VM extension on each of the VMs, or by using the Azure Resource Group Deployment task in your release pipeline to create a deployment group dynamically.
Box 2: A deployment group
References: https://docs.microsoft.com/en-us/azure/devops/pipelines/release/deployment-groups
NEW QUESTION 79
You have a private project in Azure DevOps.
You need to ensure that a project manager can create custom work item queries to report on the project's progress. The solution must use the principle of least privilege.
To which security group should you add the project manager?
- A. Reader
- B. Project Administrators
- C. Project Collection Administrators
- D. Contributor
Answer: D
Explanation:
Contributors have permissions to contribute fully to the project code base and work item tracking. The main permissions they don't have or those that manage or administer resources.
Reference:
https://docs.microsoft.com/en-us/azure/devops/organizations/security/permissions
https://docs.microsoft.com/en-us/azure/devops/organizations/security/permissions-access-work-tracking?view=azure-devops#queries-and-semantic-search
NEW QUESTION 80
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You plan to create a release pipeline that will deploy Azure resources by using Azure Resource Manager templates. The release pipeline will create the following resources:
* Two resource groups
* Four Azure virtual machines in one resource group
* Two Azure SQL databases in other resource group
You need to recommend a solution to deploy the resources.
Solution: Create two standalone templates, each of which will deploy the resources in its respective group.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Use a main template and two linked templates.
References: https://docs.microsoft.com/en-us/azure/azure-resource-manager/resource-group-linked-templates
NEW QUESTION 81
You are creating a container for an ASP.NET Core app.
You need to create a Dockerfile file to build the image. The solution must ensure that the size of the image is minimized.
How should you configure the file? To answer, drag the appropriate values to the correct targets. Each value must be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.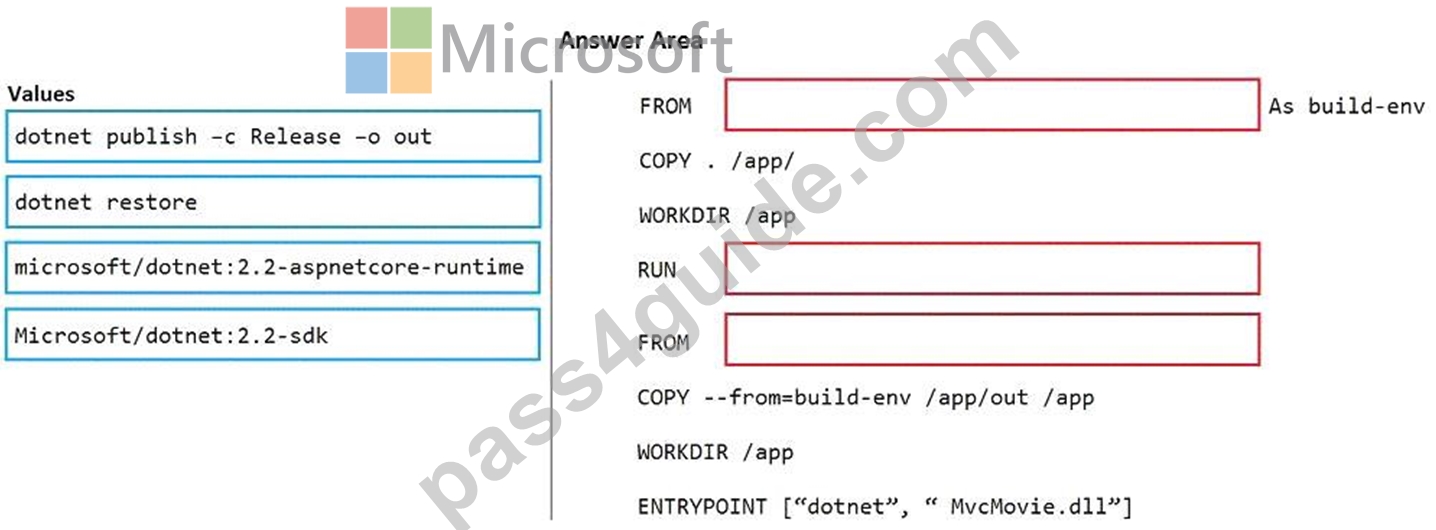
Answer:
Explanation: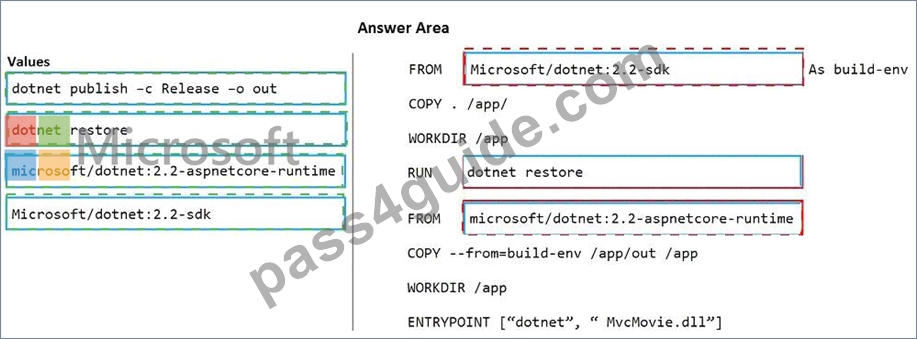
Explanation
Box 1: microsoft.com/dotnet/sdk:2.3
The first group of lines declares from which base image we will use to build our container on top of. If the local system does not have this image already, then docker will automatically try and fetch it. The mcr.microsoft.com/dotnet/core/sdk:2.1 comes packaged with the .NET core 2.1 SDK installed, so it's up to the task of building ASP .NET core projects targeting version 2.1 Box 2: dotnet restore The next instruction changes the working directory in our container to be /app, so all commands following this one execute under this context.
COPY *.csproj ./
RUN dotnet restore
Box 3: microsoft.com/dotnet/2.2-aspnetcore-runtime
When building container images, it's good practice to include only the production payload and its dependencies in the container image. We don't want the .NET core SDK included in our final image because we only need the .NET core runtime, so the dockerfile is written to use a temporary container that is packaged with the SDK called build-env to build the app.
Reference:
https://docs.microsoft.com/de-DE/virtualization/windowscontainers/quick-start/building-sample-app
NEW QUESTION 82
You mc configuring Azure DevOps build pipelines.
You plan to use hosted build agents.
Which build agent pool should you use to compile each application type? To answer, drag the appropriate built agent pools to the correct application types. Each butt agent pool may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Hosted macOS
Hosted macOS pool (Azure Pipelines only): Enables you to build and release on macOS without having to configure a self-hosted macOS agent. This option affects where your data is stored.
Box 2: Hosted
Hosted pool (Azure Pipelines only): The Hosted pool is the built-in pool that is a collection of Microsoft-hosted agents.
Incorrect Answers:
Default pool: Use it to register self-hosted agents that you've set up.
Hosted Windows Container pool (Azure Pipelines only): Enabled you to build and release inside Windows containers. Unless you're building using containers, Windows builds should run in the Hosted VS2017 or Hosted pools.
References:
https://docs.microsoft.com/en-us/azure/devops/pipelines/agents/v2-osx
NEW QUESTION 83
You have a protect in Azure DevOps.
You need to associate an automated test to a test case.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.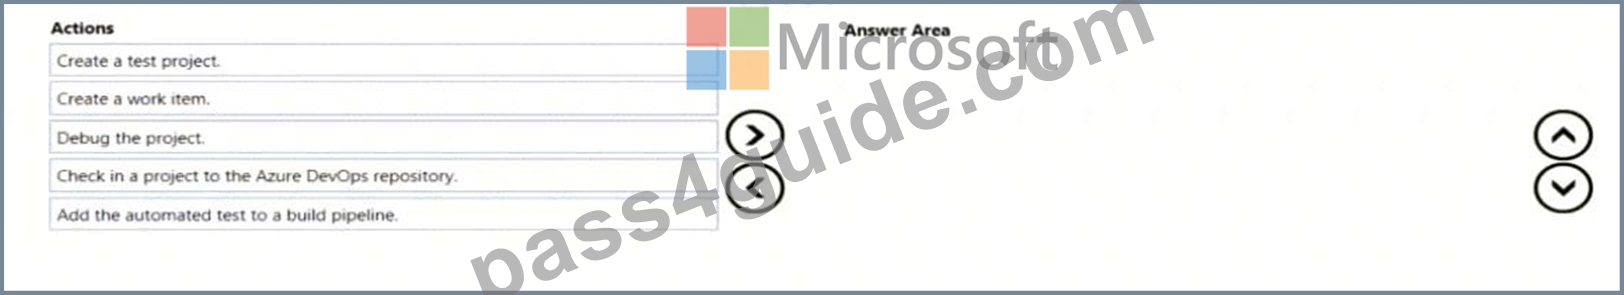
Answer:
Explanation:
Explanation
NEW QUESTION 84
You are implementing a package management solution for a Node.js application by using Azure Artifacts.
You need to configure the development environment to connect to the package repository. The solution must minimize the likelihood that credentials will be leaked.
Which file should you use to configure each connection? To answer, drag the appropriate files to the correct connections. Each file may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
All Azure Artifacts feeds require authentication, so you'll need to store credentials for the feed before you can install or publish packages. npm uses .npmrc configuration files to store feed URLs and credentials. Azure DevOps Services recommends using two .npmrc files.
Feed registry information: The .npmrc file in the project
One .npmrc should live at the root of your git repo adjacent to your project's package.json. It should contain a "registry" line for your feed and it should not contain credentials since it will be checked into git.
Credentials: The .npmrc file in the user's home folder
On your development machine, you will also have a .npmrc in $home for Linux or Mac systems or $env.HOME for win systems. This .npmrc should contain credentials for all of the registries that you need to connect to. The NPM client will look at your project's .npmrc, discover the registry, and fetch matching credentials from $home/.npmrc or $env.HOME/.npmrc.
References:
https://docs.microsoft.com/en-us/azure/devops/artifacts/npm/npmrc?view=azure-devops&tabs=windows
NEW QUESTION 85
You plan to share packages that you wrote, tested, validated, and deployed by using Azure Artifacts.
You need to release multiple builds of each package by using a single feed. The solution must limit the release of packages that are in development.
What should you use?
- A. global symbols
- B. local symbols
- C. upstream sources
- D. views
Answer: C
Explanation:
Explanation
Upstream sources enable you to manage all of your product's dependencies in a single feed. We recommend publishing all of the packages for a given product to that product's feed, and managing that product's dependencies from remote feeds in the same feed, via upstream sources. This setup has a few benefits:
* Simplicity: your NuGet.config, .npmrc, or settings.xml contains exactly one feed (your feed).
* Determinism: your feed resolves package requests in order, so rebuilding the same codebase at the same commit or changeset uses the same set of packages
* Provenance: your feed knows the provenance of packages it saved via upstream sources, so you can verify that you're using the original package, not a custom or malicious copy published to your feed
* Peace of mind: packages used via upstream sources are guaranteed to be saved in the feed on first use; if the upstream source is disabled/removed, or the remote feed goes down or deletes a package you depend on, you can continue to develop and build References: https://docs.microsoft.com/en-us/azure/devops/artifacts/concepts/upstream-sources?view=vsts
NEW QUESTION 86
You need to create deployment files for an Azure Kubernetes Service (AKS) cluster. The deployments must meet the provisioning storage requirements shown in the following table.
Which resource type should you use for each deployment? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Deployment 1: Kubernetes.io/azure-file
You can use Azure Files to connect using the Server Message Block (SMB) protocol.
Deployment 2: Kubernetes.io/azure-disk
Deployment 3: azurekeyvault-flexvolume
azurekeyvault-flexvolume: Key Vault FlexVolume: Seamlessly integrate your key management systems with Kubernetes.
Secrets, keys, and certificates in a key management system become a volume accessible to pods. Once the volume is mounted, its data is available directly in the container filesystem for your application.
NEW QUESTION 87
......
Guaranteed Success in Microsoft Azure AZ-400 Exam Dumps: https://www.pass4guide.com/AZ-400-exam-guide-torrent.html
AZ-400 Practice Test Engine: Try These 329 Exam Questions: https://drive.google.com/open?id=1nqxTFXpDbg5RxIAIwfE300319LUBz5oj